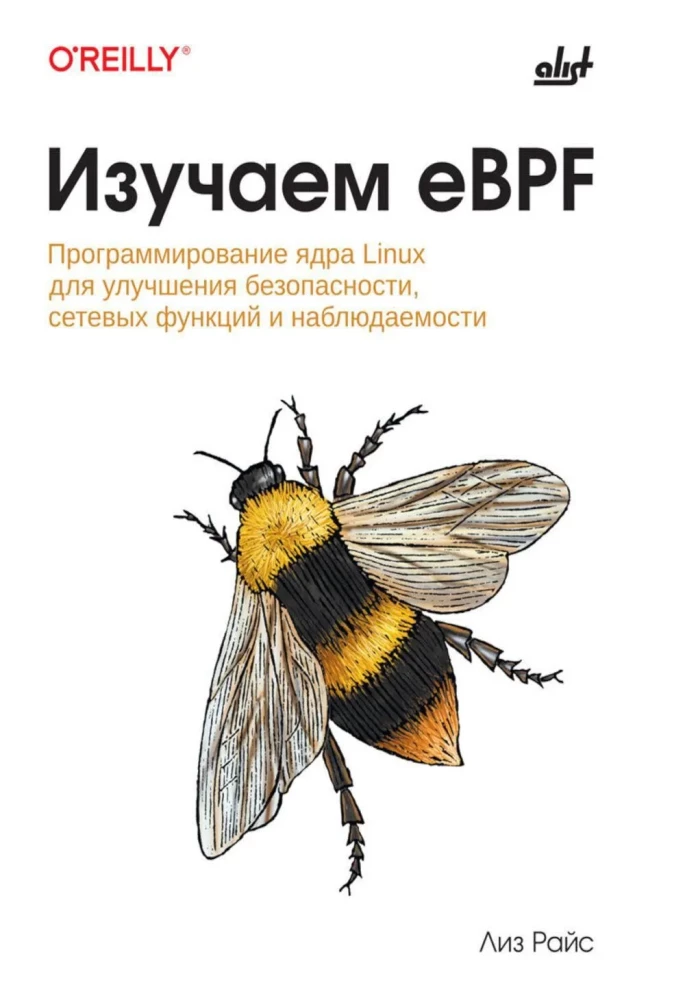
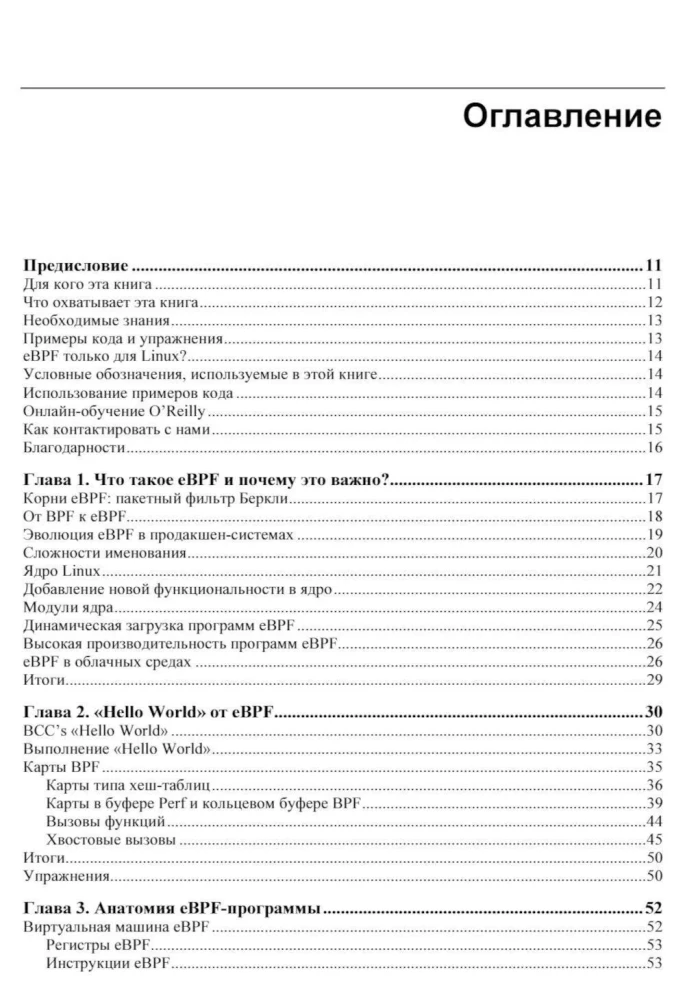
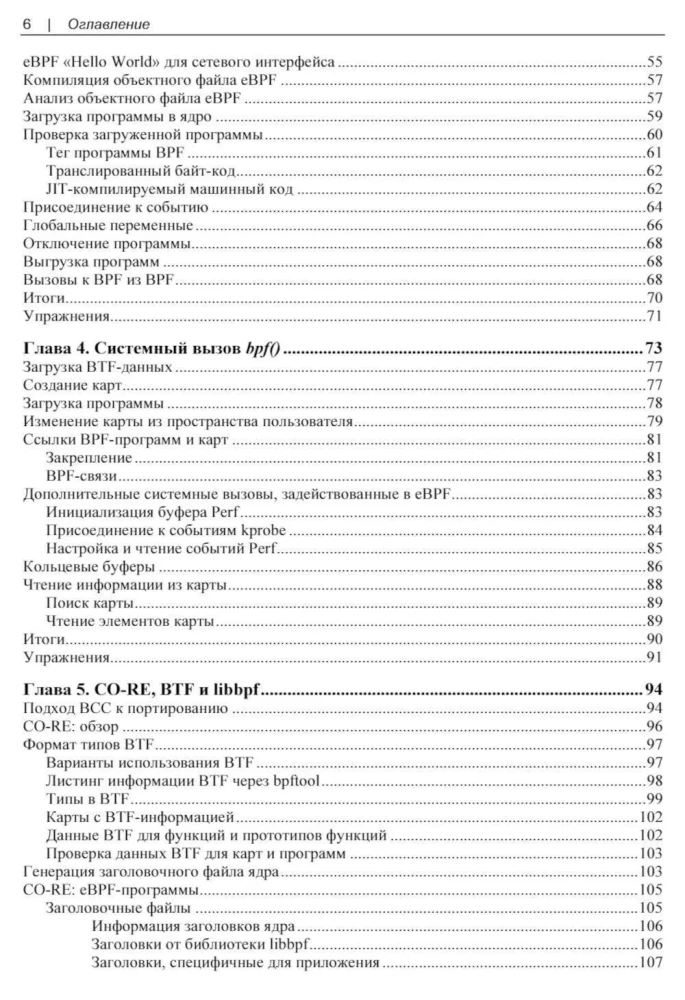
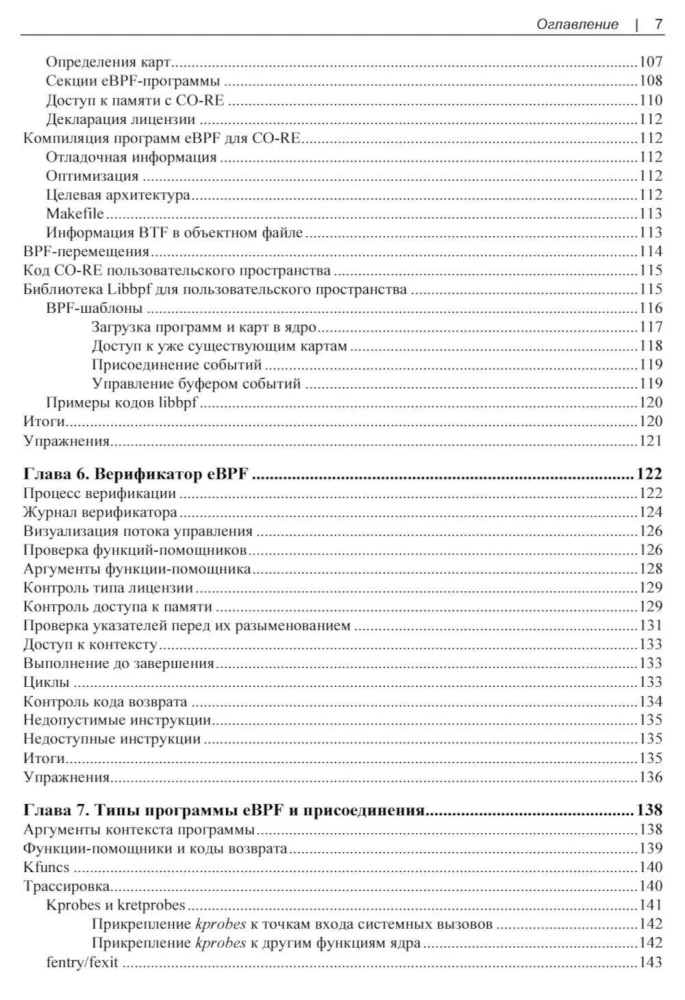
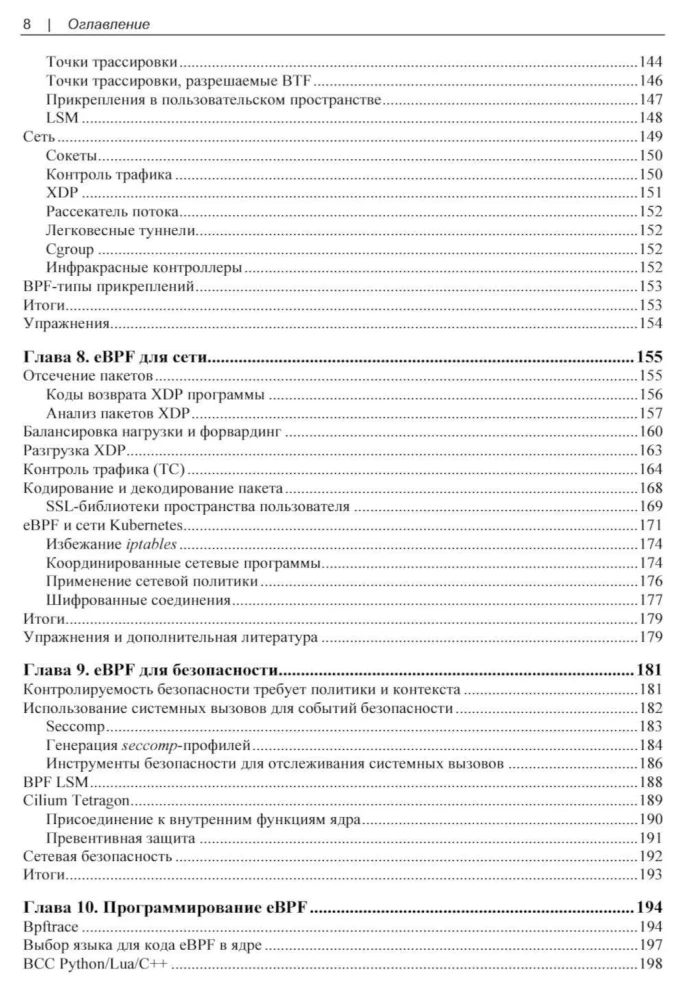
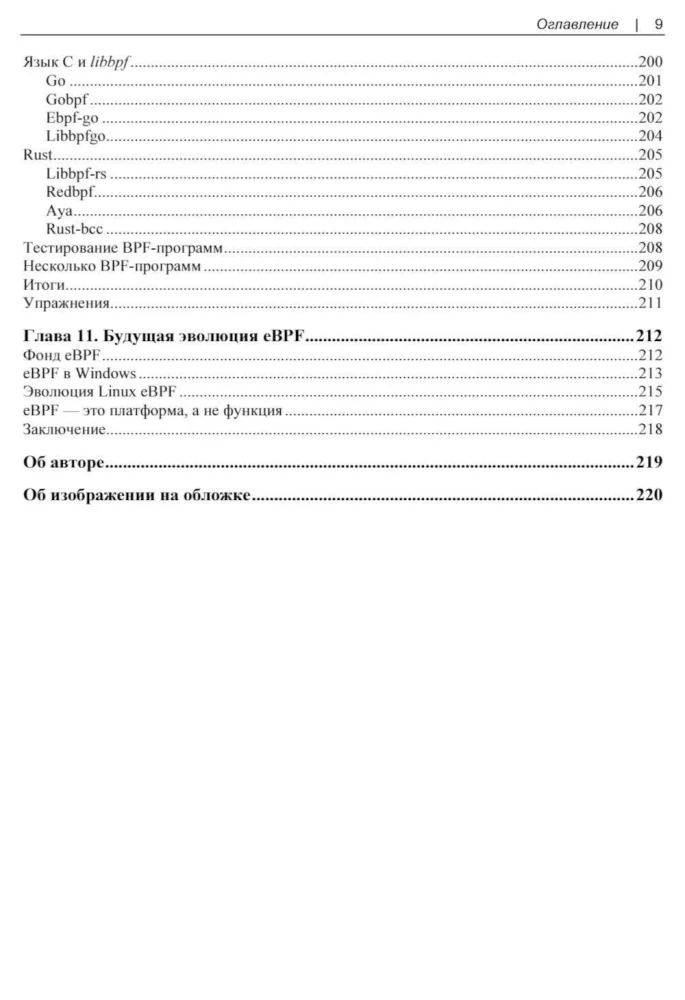
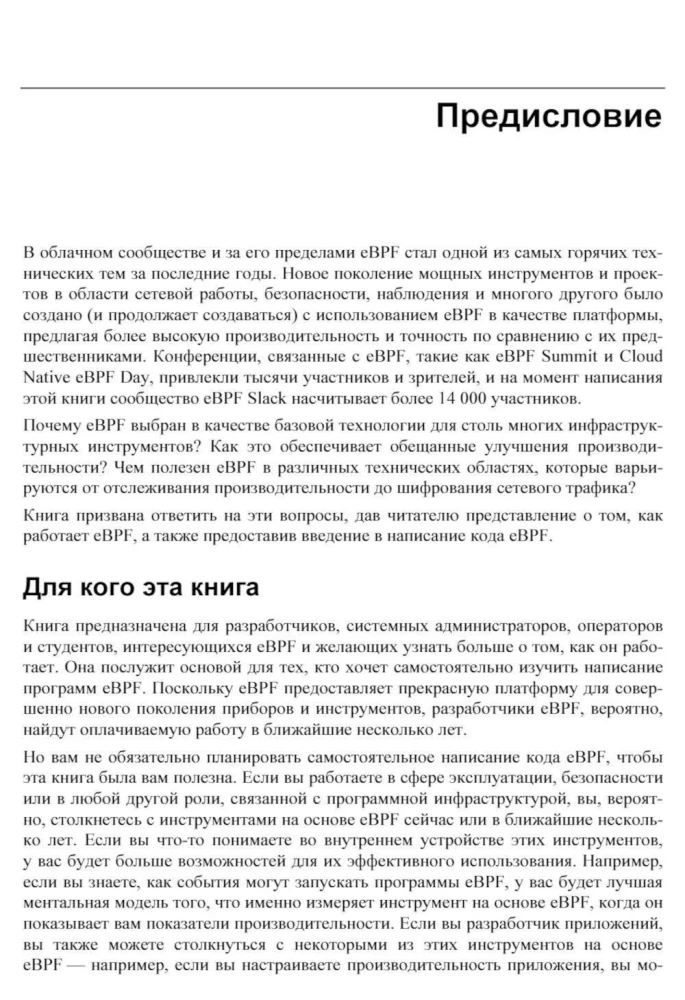
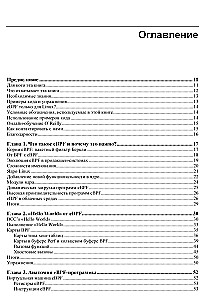
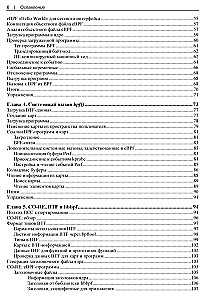
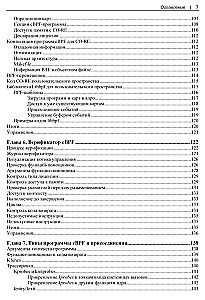
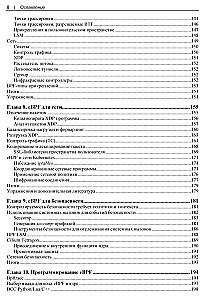
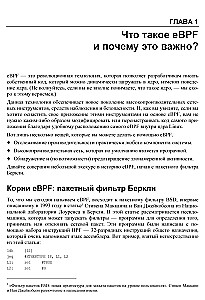
A book on eBPF technology, built on the famous packet filter invented at the University of Berkeley (Berkeley Packet Filter), allowing user packets to pass into the Linux kernel and thus modify the behavior and functions of the kernel. The book discusses how eBPF relates to the structure of the Linux kernel and its extensions, which system calls are used when servicing eBPF, and the role eBPF plays in ensuring security. It covers programming modules for eBPF and explains practical aspects of using this mechanism: porting programs from distribution to distribution and from corporate servers to the cloud.
Sold out
€ 14.49
Sold out
€ 14.49
Bestsellers
€ 11.59
In stock
We Are Right for Each Other: How Attachment Theory Can Help Create Harmonious Relationships
Амир Левин, Рэйчел Хеллер
€ 11.99
In stock
Invisible Women: Why We Live in a World Designed for Men. Data Bias in a World Designed for Men
Кэролайн Криадо Перес
€ 6.99
In stock
How to Talk So Kids Will Listen, and How to Listen So Kids Will Talk
Элейн Мазлиш, Адель Фабер